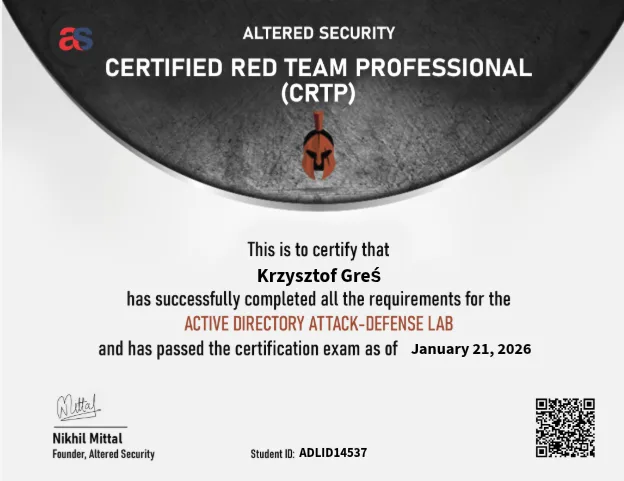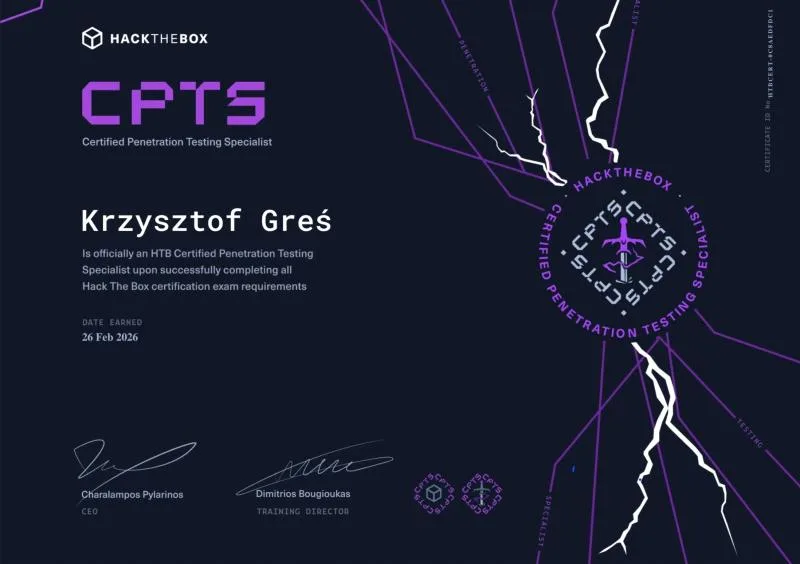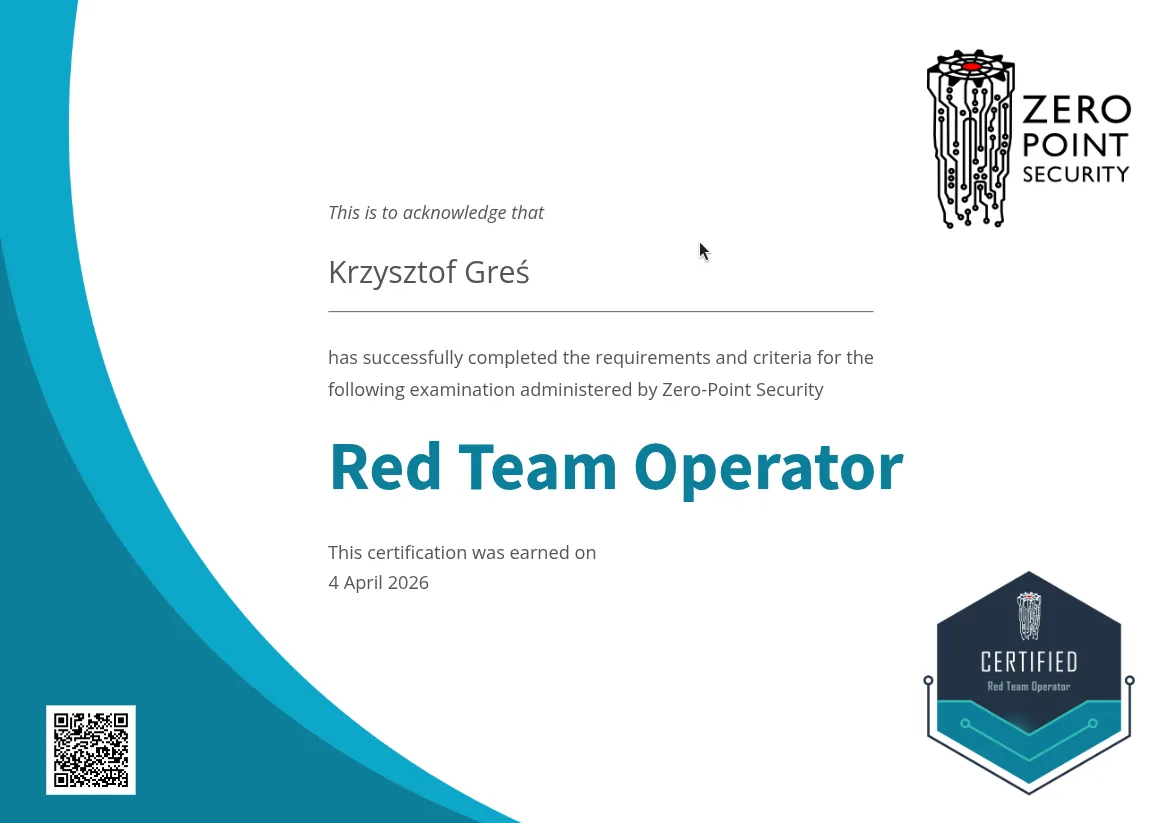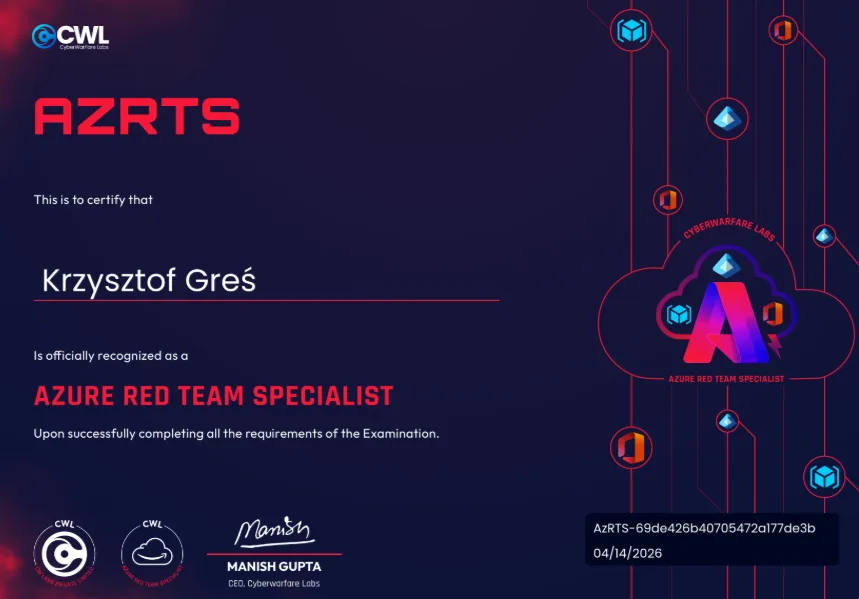
I’m Krzysztof Greś (h4mr3r), a red team specialist and malware developer based in Poland. For more than five years I have worked in enterprise offensive security consulting — first at KPMG Poland, now as a Senior Cyber Security Consultant at Netia S.A. — running red team operations, penetration tests, and adversary simulations.
Through Security Buffor I offer that work as authorized engagements: realistic attacks, run under strict rules of engagement, that show where defenses hold, where they fail, and what to fix first.
What I Do
I work across the offensive security spectrum with expertise in:
- Red Teaming — objective-led operations that emulate advanced persistent threats across Active Directory, Azure, and physical and network breach scenarios.
- Penetration Testing — internal and external infrastructure assessments that find and chain critical vulnerabilities.
- Malware Development — evasive payloads, custom command-and-control (C2) tooling, and low-level tradecraft for authorized operations.
Current Projects
Right now I’m focused on:
- AXIOM — professional security reporting toolkit
- SIPHON — social-engineering operations toolkit
Experience
Netia S.A.
Poland
Oct 2025 - PRESENT
- Senior Cyber Security Consultant Oct 2025 - PRESENT
Leading advanced adversary simulations and enhancing the organization's defensive posture through targeted red team operations and custom malware development
KPMG Poland
Poland
Jul 2021 – Oct 2025
- Senior Cyber Security Consultant Oct 2024 – Oct 2025
- Cyber Security Consultant Apr 2023 – Oct 2024
- Cyber Security Junior Consultant Jan 2022 – Apr 2023
- Cyber Security Intern Jul 2021 – Jan 2022
Progressed from security internship to senior consulting responsibilities across enterprise penetration testing, red team engagements, vulnerability assessments, and stakeholder-facing security reporting.
Certifications